
Frost & Sullivan named Oligo the 2026 Global Company of the Year in application detection and response. The report examines the runtime blind spot that SCA, ASPM, and CNAPP leave open, and how Oligo closes it with function-level visibility, high-fidelity detections, and exploit blocking that keeps applications running.
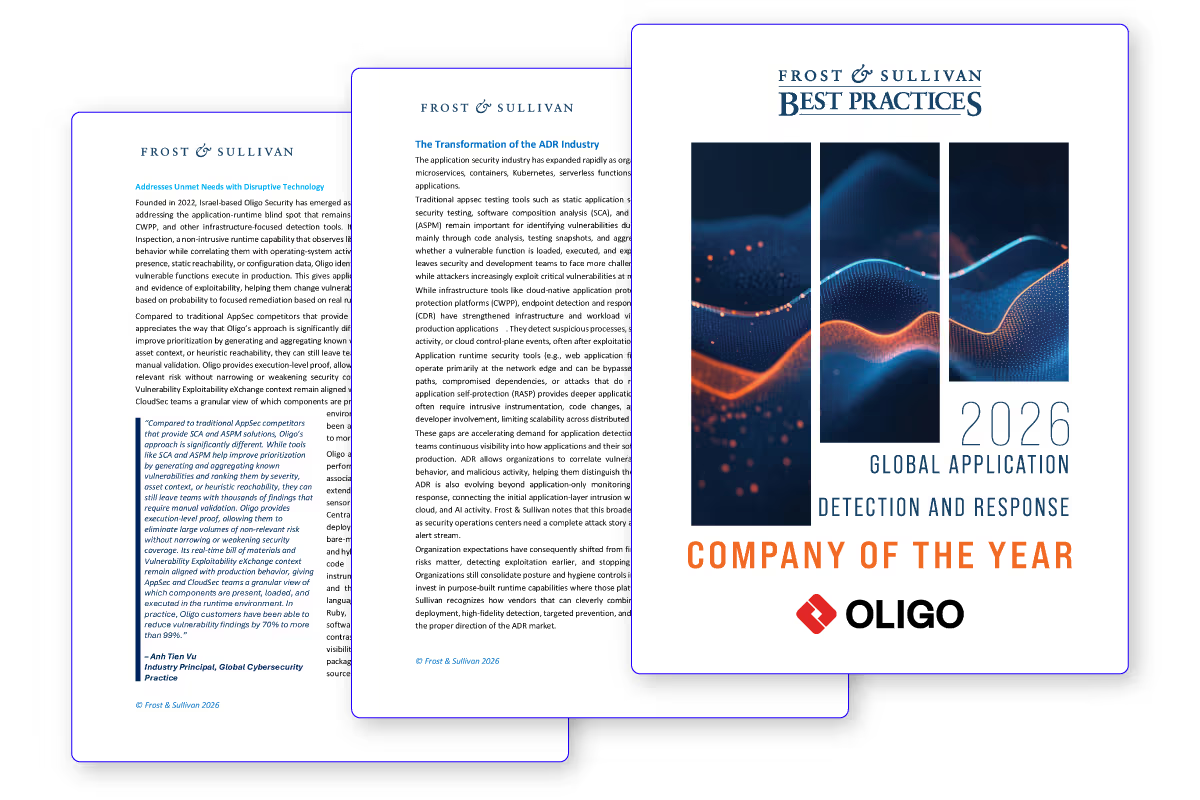
SCA flags vulnerable packages, SAST flags risky code, and ASPM ranks the results. None can tell you whether that code loads or executes in production.
Customers report 70% to 99% fewer vulnerability findings. Oligo goes live in hours or days with no code changes or restarts, and delivers SOC-ready incidents with call stacks, process trees, and MITRE ATT&CK context.
Frost and Sullivan points out a key strength for Oligo: its ability to tie system actions to the exact functions and libraries that triggered them, across software that customers build, buy, or run without requiring source code access.
Runtime Exploit Blocking stops the malicious action at the point of execution while the app keeps running. Because it targets exploit techniques rather than payload signatures, one rule covers entire vulnerability classes, including previously unknown attacks.
2026 Company of the Year
Share it with your AppSec, CloudSec, and SOC leads before your next tooling review.
