We see and stop malicious code execution. While traditional tools scan for static vulnerabilities or monitor networks, attackers exploit your biggest blind spot: code running in production. Stop guessing. Start defending.
Schedule a 1:1 Meeting at Black Hat 2026


Your CNAPP is great at scanning code before it goes live, and your EDR secures your endpoints—but neither can tell you what is actually happening inside your applications during runtime. Attackers exploit this massive visibility gap to inject malicious code into third-party libraries and compromise your software supply chain.


Join the Oligo team for a live demo of our Runtime Security Platform!
Stop by our booth to see our technology in action and talk to our core engineering and security experts.
Learn how Oligo:

Attackers have found a new way to scale: hijack your AI infrastructure and turn it into the attack vector.
Join Avi Lumelsky and Gal Elbaz from Oligo as they reveal how a global campaign exploited exposed Ray clusters across 230,000+ servers using compromised AI compute to autonomously target and infect other AI environments.
Join them at Black Hat USA 2026 to understand what this attack class means for your AI infrastructure posture.


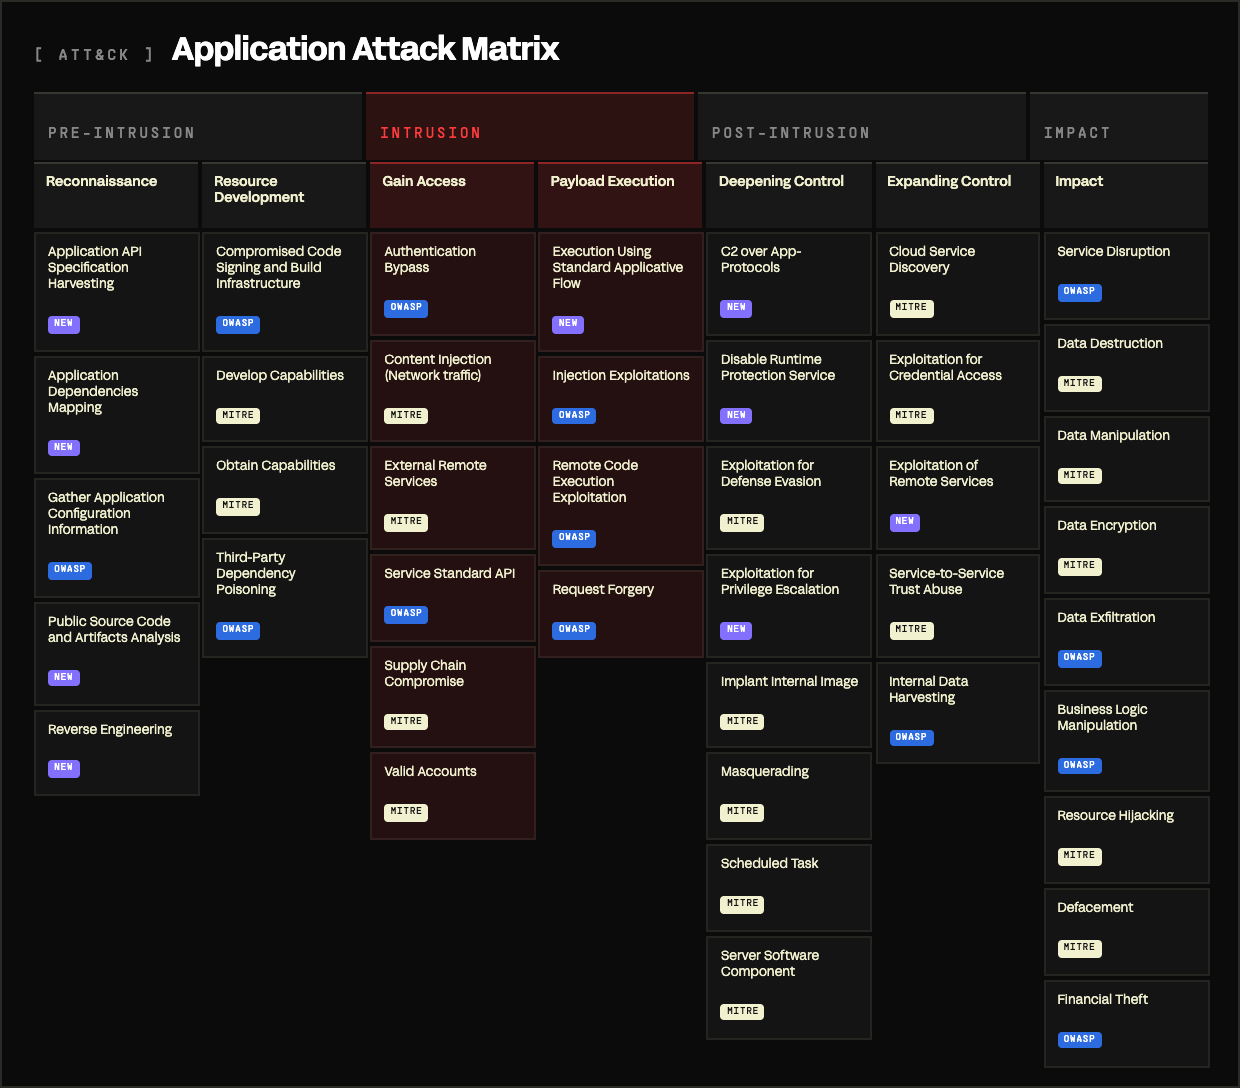
Shared threat frameworks have enabled consistent communication and coordination across vulnerability researchers, PSIRTs, vendors, and defenders. However, as attackers increasingly operate at the application layer (abusing software supply chains, runtime behavior, and trusted cloud workflows) defenders face challenges applying existing models consistently. This session presents lessons from the Application Attack Matrix, a community-driven research effort involving contributors from Mandiant (Google Cloud), Microsoft, AWS, Meta, Oligo Security, and others, and uses the ByBit / Safe{Wallet} incident to illustrate why application-layer technique modeling is increasingly important.
Oligo’s Runtime Security platform delivers the missing piece of your security stack: