
Java4Shell Zero-Day. Blocked by Oligo.
A critical memory corruption vulnerability in Java's core. Oligo blocks exploitation at runtime, before applications are patched.
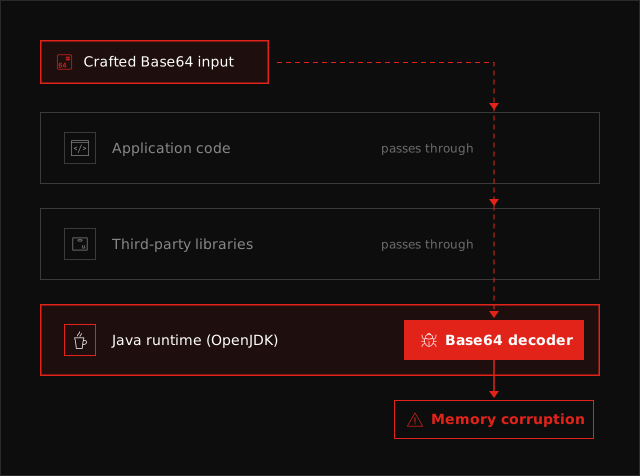
Java4Shell (CVE-2026-114938) targets OpenJDK's Base64 decoder, potentially exposing Java applications running on affected x86 systems.
Oligo has developed runtime protection to stop exploitation of the vulnerable code path while allowing legitimate application activity to continue.
Watch Oligo Block Java4Shell

Agent visibility
•
Runtime control
•
Failure containment
What Is Java4Shell?
Java4Shell is a zero-day memory corruption vulnerability in Java's built-in Base64 decoder.
Unlike a vulnerable third-party library, the flaw exists inside the Java runtime itself. Applications processing maliciously crafted Base64 input may be exposed.
Are Your Applications Vulnerable?
Exposure depends on your Java version, x86 processor configuration, and whether untrusted input can reach the vulnerable decoding path.
Knowing you run Java isn't enough. You need to understand what's happening inside your applications.
How Oligo Blocks Java4Shell
Block the Exploit. Keep Java Running.
Oligo's runtime protection targets Java4Shell exploitation where it happens: inside the running application.
Stop exploitation:
Block attempts to trigger the vulnerable decoding path.
Keep applications running:
Allow legitimate Java operations to continue.
Protect before patching:
Add protection while security teams assess exposure and roll out updates.
No waiting for a patch to begin protecting production.
The Next Zero-Day Won't Wait. Neither Should Your Defense.
Java4Shell is another reminder that critical vulnerabilities can emerge in the software your applications rely on most.Oligo blocks exploits at runtime, helping protect applications during the gap between discovery and remediation.

