
Oligo + Wiz: Runtime Proof Meets Cloud Context

Security teams running Wiz can now enrich every vulnerability finding with deterministic runtime evidence from Oligo. The joint integration ingests Oligo's execution telemetry directly into Wiz, so cloud and application security teams see which vulnerable libraries are actually loaded and invoked in production, right alongside the posture context Wiz already provides.
Why vulnerability backlogs keep growing
Modern cloud environments generate vulnerability findings faster than any team can triage them. Container scans, SBOM analysis, and reachability estimates all produce long lists of CVEs ranked by CVSS scores and static assumptions about what might be exploitable. Security teams spend weeks working through backlogs, developers push back on findings they suspect are dormant, and remediation slows to a crawl while real exposure sits somewhere inside the queue.
The gap is proof. Without runtime evidence, teams cannot separate the vulnerabilities that will actually be exploited from the ones sitting in code paths that never execute.
What Wiz brings
Wiz has become the reference standard for cloud and AI posture. It maps assets, identities, misconfigurations, and exposure paths across the environment with a depth that few tools match, and it gives security teams a single place to reason about cloud risk. Wiz already surfaces application context and reachability signals that help prioritize findings across the estate.
What Oligo adds
Oligo observes what is actually running inside applications, cloud workloads, and AI systems in production. When a vulnerable library sits in a container image, Oligo determines whether that library is loaded into memory, executed, and whether the specific vulnerable function is being invoked by the running application. This is the layer beneath cloud posture, and it is the layer where exploitation actually happens.
The integration surfaces that state directly inside Wiz workflows, so teams get the full picture without leaving the tool they already use.
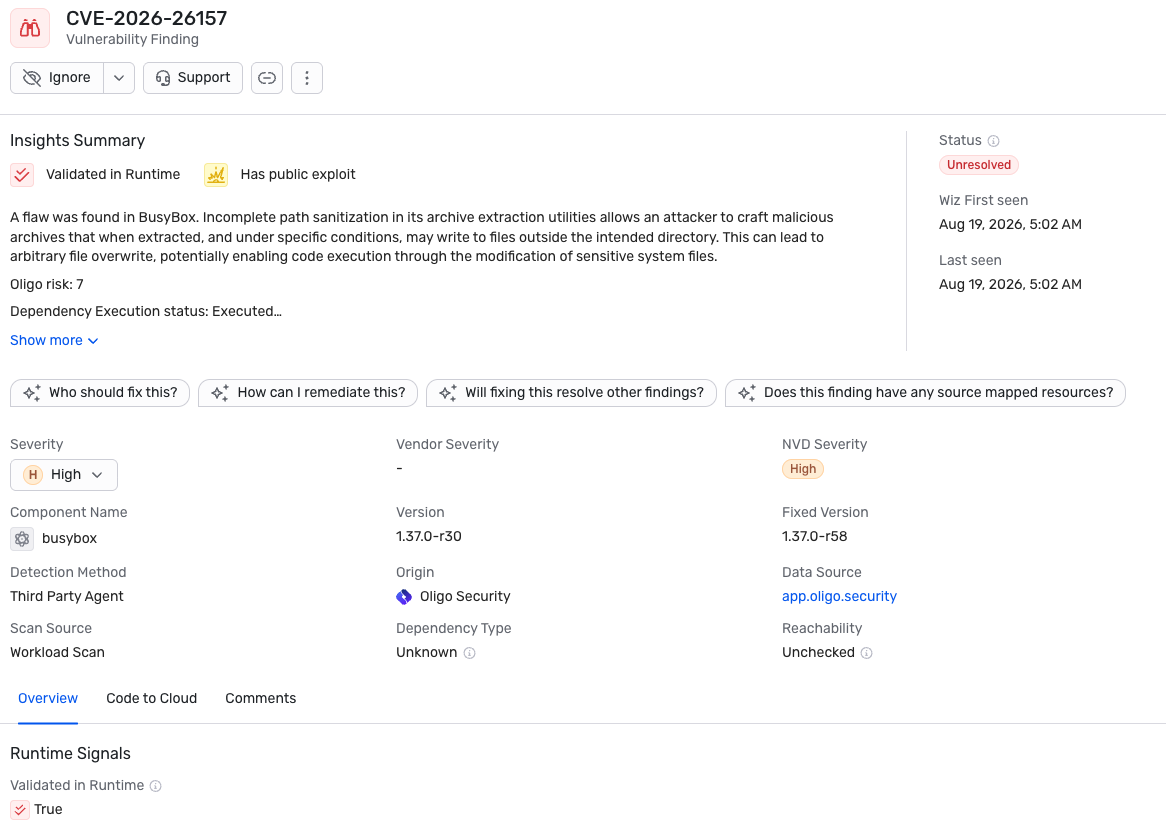
What each team gets
Cloud Security keeps its Wiz-centered workflow and gains runtime proof that turns theoretical exposure into a ranked list of real, exploitable risk across workloads.
AppSec stops chasing CVEs that live in dormant code paths, and can point developers to the small subset of findings that reach production execution, with call stacks and function-level evidence to back the ask.
CISOs and security leaders see backlogs shrink by 90 percent or more, cross-team friction drop, and mean time to remediation compress, without new tools for engineering to learn or new friction for the business to absorb.
Cloud posture, application runtime, one workflow
The integration reflects how modern security actually works. Wiz answers what exists across the cloud and AI environment and how it is exposed. Oligo answers what is running and what is exploitable. Together, they close the loop from the environment down to the executing code, and give security teams the evidence to act with confidence.
The Oligo integration for Wiz is available now.
Stop modern attacks and keep your business moving


